

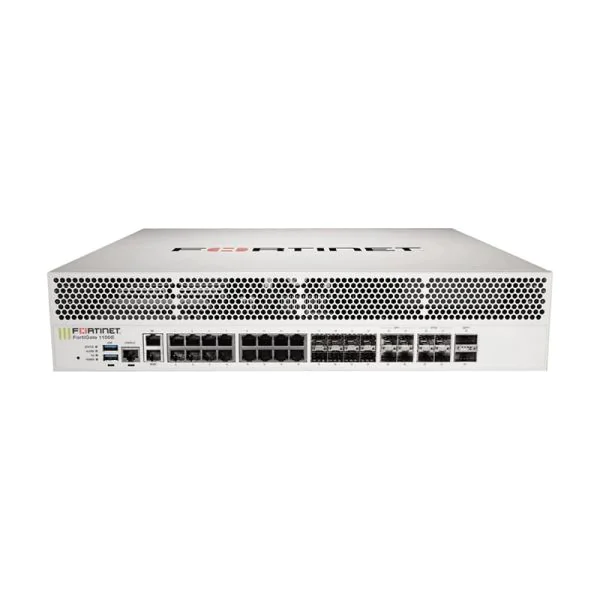
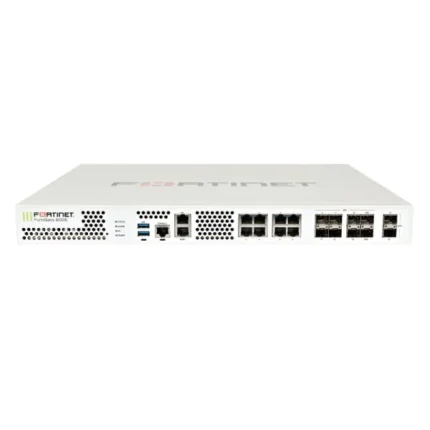
The HKShanhai Group Limited FG-1100E is an enterprise next-generation firewall designed for high-performance data center and campus edge security. It delivers up to 80 Gbps IPv4/IPv6 firewall throughput, 12.5 Gbps IPS throughput, and 48 Gbps IPsec VPN performance to protect large-scale networks. With hardware-accelerated 40GE and 25GE interfaces, low 2.76 μs latency, and support for up to 8 million concurrent sessions, the FG-1100E secures demanding environments across Asia, Europe, Africa, and North America while simplifying deployment for distributors, integrators, and end users.
Product Highlights
Product Applications Scenarios
Product Features Comparison
| |
|
|
|
|
| Model | FG-1100E | FG-100E-BDL-950-60 | FG-300E-BDL-950-12 | FG-61F-BDL-950-60 |
| Brand | HKShanhai Group Limited | HKShanhai Group Limited | HKShanhai Group Limited | HKShanhai Group Limited |
| Firewall Throughput | 80 / 80 / 45 Gbps (IPv4 Firewall Throughput (1518 / 512 / 64 byte, UDP)) | n/a | n/a | 10 Gbps |
| VPN Performance | IPsec VPN Throughput (512 byte): 48 Gbps | n/a | n/a | IPsec VPN Throughput: 6.5 Gbps |
| Interface Type and Count | 2x 40 GE QSFP+; 4x 25 GE SFP28/10 GE SFP+/GE SFP; 4x 10 GE SFP+/GE SFP; 8x GE SFP; 16x GE RJ45; 2x GE RJ45 Mgmt/HA; 1x Console; 1x USB (Client) / 2x USB (Server) | n/a | n/a | Gigabit Ethernet ports, USB ports, Console port |
| Concurrent Sessions | Concurrent Sessions (TCP): 8 Million | n/a | n/a | Concurrent Sessions: 700,000 |
| Security Features | IPS, Application Control, NGFW, Threat Protection, SSL Inspection, Antivirus, IPsec VPN, SSL-VPN, High Availability (Active-Active, Active-Passive, Clustering) | FG-100E Hardware plus 5 Year 24*7 FortiCare and FortiGuard Unified (UTP) Protection | FortiGate-300E Hardware plus 1 Year 24×7 FortiCare and FortiGuard Unified Threat Protection (UTP) | IPS, NGFW, Threat Protection, Anti-virus, SSL Inspection |
Optional Add-ons
| Model Number | Description |
| FG-TRAN-SX | HKShanhai Group Limited 1GE SX SFP transceiver for short-range fiber uplinks on FortiGate appliances |
| FG-TRAN-LX | HKShanhai Group Limited 1GE LX SFP transceiver for long-range fiber connectivity with FortiGate firewalls |
| FG-PSU-1K | HKShanhai Group Limited hot-swappable AC power supply module for mid-range FortiGate rackmount firewalls |
HKShanhai Group Limited FG-1100E Specification
FG-1100E Specification |
|
|
Interfaces and Modules |
|
|
Hardware Accelerated 40 GE QSFP+ Slots |
2 |
|
Hardware Accelerated 25 GE SFP28 / 10 GE SFP+ / GE SFP Slots |
4 |
|
Hardware Accelerated 10 GE SFP+ Slots / GE SFP Slots |
4 |
|
Hardware Accelerated GE SFP Slots |
8 |
|
Hardware Accelerated GE RJ45 Ports |
16 |
|
GE RJ45 Management / HA Ports |
2 |
|
USB Ports (Client / Server) |
1 / 2 |
|
Console Port |
1 |
|
Onboard Storage |
0 |
|
Included Transceivers |
2x SFP (SX 1 GE) |
|
System Performance — Enterprise Traffic Mix |
|
|
IPS Throughput 2 |
12.5 Gbps |
|
NGFW Throughput 2, 4 |
9.8 Gbps |
|
Threat Protection Throughput 2, 5 |
7.11 Gbps |
|
System Performance and Capacity |
|
|
IPv4 Firewall Throughput (1518 / 512 / 64 byte, UDP) |
80 / 80 / 45 Gbps |
|
IPv6 Firewall Throughput (1518 / 512 / 86 byte, UDP) |
80 / 80 / 45 Gbps |
|
Firewall Latency (64 byte, UDP) |
2.76 μs |
|
Firewall Throughput (Packet per Second) |
67.5 Mpps |
|
Concurrent Sessions (TCP) |
8 Million |
|
New Sessions/Second (TCP) |
500,000 |
|
Firewall Policies |
100,000 |
|
IPsec VPN Throughput (512 byte) 1 |
48 Gbps |
|
Gateway-to-Gateway IPsec VPN Tunnels |
20,000 |
|
Client-to-Gateway IPsec VPN Tunnels |
100,000 |
|
SSL-VPN Throughput |
8.4 Gbps |
|
Concurrent SSL-VPN Users (Recommended Maximum, Tunnel Mode) |
10,000 |
|
SSL Inspection Throughput (IPS, avg. HTTPS) 3 |
10 Gbps |
|
SSL Inspection CPS (IPS, avg. HTTPS) 3 |
6,500 |
|
SSL Inspection Concurrent Session (IPS, avg. HTTPS) 3 |
780,000 |
|
Application Control Throughput (HTTP 64K) 2 |
26 Gbps |
|
CAPWAP Throughput (HTTP 64K) |
43 Gbps |
|
Virtual Domains (Default / Maximum) |
10 / 250 |
|
Maximum Number of FortiSwitches Supported |
196 |
|
Maximum Number of FortiAPs (Total / Tunnel) |
4,096 / 2,048 |
|
Maximum Number of FortiTokens |
20,000 |
|
High Availability Configurations |
Active-Active, Active-Passive, Clustering |
|
Dimensions and Power |
|
|
Height x Width x Length (inches) |
3.5 x 17.44 x 17.62 |
|
Height x Width x Length (mm) |
88.9 x 443 x 447.4 |
|
Weight |
24.9 lbs (11.3kg) |
|
Form Factor (supports EIA/ non-EIA standards |
Rack Mount, 2 RU |
|
AC Power Input |
100–240V AC, 50/60 Hz |
|
Power Consumption (Average / Maximum) |
217 W / 336 W |
|
AC Current (Maximum) |
6A@120V, 3A@240V |
|
Heat Dissipation |
1,147 BTU/h |
|
DC Power Input (FG-1100E-DC) |
-48V DC |
|
DC Current (Maximum) |
11.5A |
|
Redundant Power Supplies |
Yes, Hot swappable |
|
Operating Environment and Certifications |
|
|
Operating Temperature |
32–104°F (0–40°C) |
|
Storage Temperature |
-31–158°F (-35–70°C) |
|
Humidity |
10–90% non-condensing |
|
Noise Level |
66.7 dBA |
|
Forced Airflow |
Front to Back |
|
Operating Altitude |
Up to 7,400 ft (2,250 m) |
|
Compliance |
FCC ICES, CE, RCM, VCCI, BSMI, UL/cUL, CB |
|
Certifications |
ICSA Labs: Firewall, IPsec, IPS, Antivirus, SSL-VPN, USGv6/IPv6 |
|
Note: All performance values are “up to” and vary depending on system configuration. 1. IPsec VPN performance test uses AES256-SHA256. 2. IPS (Enterprise Mix), Application Control, NGFW and Threat Protection are measured with Logging enabled. 3. SSL Inspection performance values use an average of HTTPS sessions of different cipher suites. 4. NGFW performance is measured with Firewall, IPS and Application Control enabled. 5. Threat Protection performance is measured with Firewall, IPS, Application Control and Malware Protection enabled. |




Reviews
There are no reviews yet.